Software
Shadow Force Uses DLL Hijacking, Targets South Korean Company
Reported by blog.trendmicro.com
What sort of interest would a businessman have in a news agency?
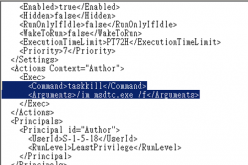
That was the question that arose from our recent investigation on an attack that appears to target a media agency in South Korea. Shadow Force is a new backdoor that replaces a DLL called by a particular Windows service. Once that backdoor is open, the attacker can use one or more tools to open up further holes or cause damage. This type of backdoor attack has been previously documented by Trend Micro in a blog post in May.